Your customer list could cost you RM1 million.
Hold data on 20,000+ people? You now need a Data Protection Officer and a plan to report breaches within 72 hours. Fines for mishandling personal data have more than tripled.
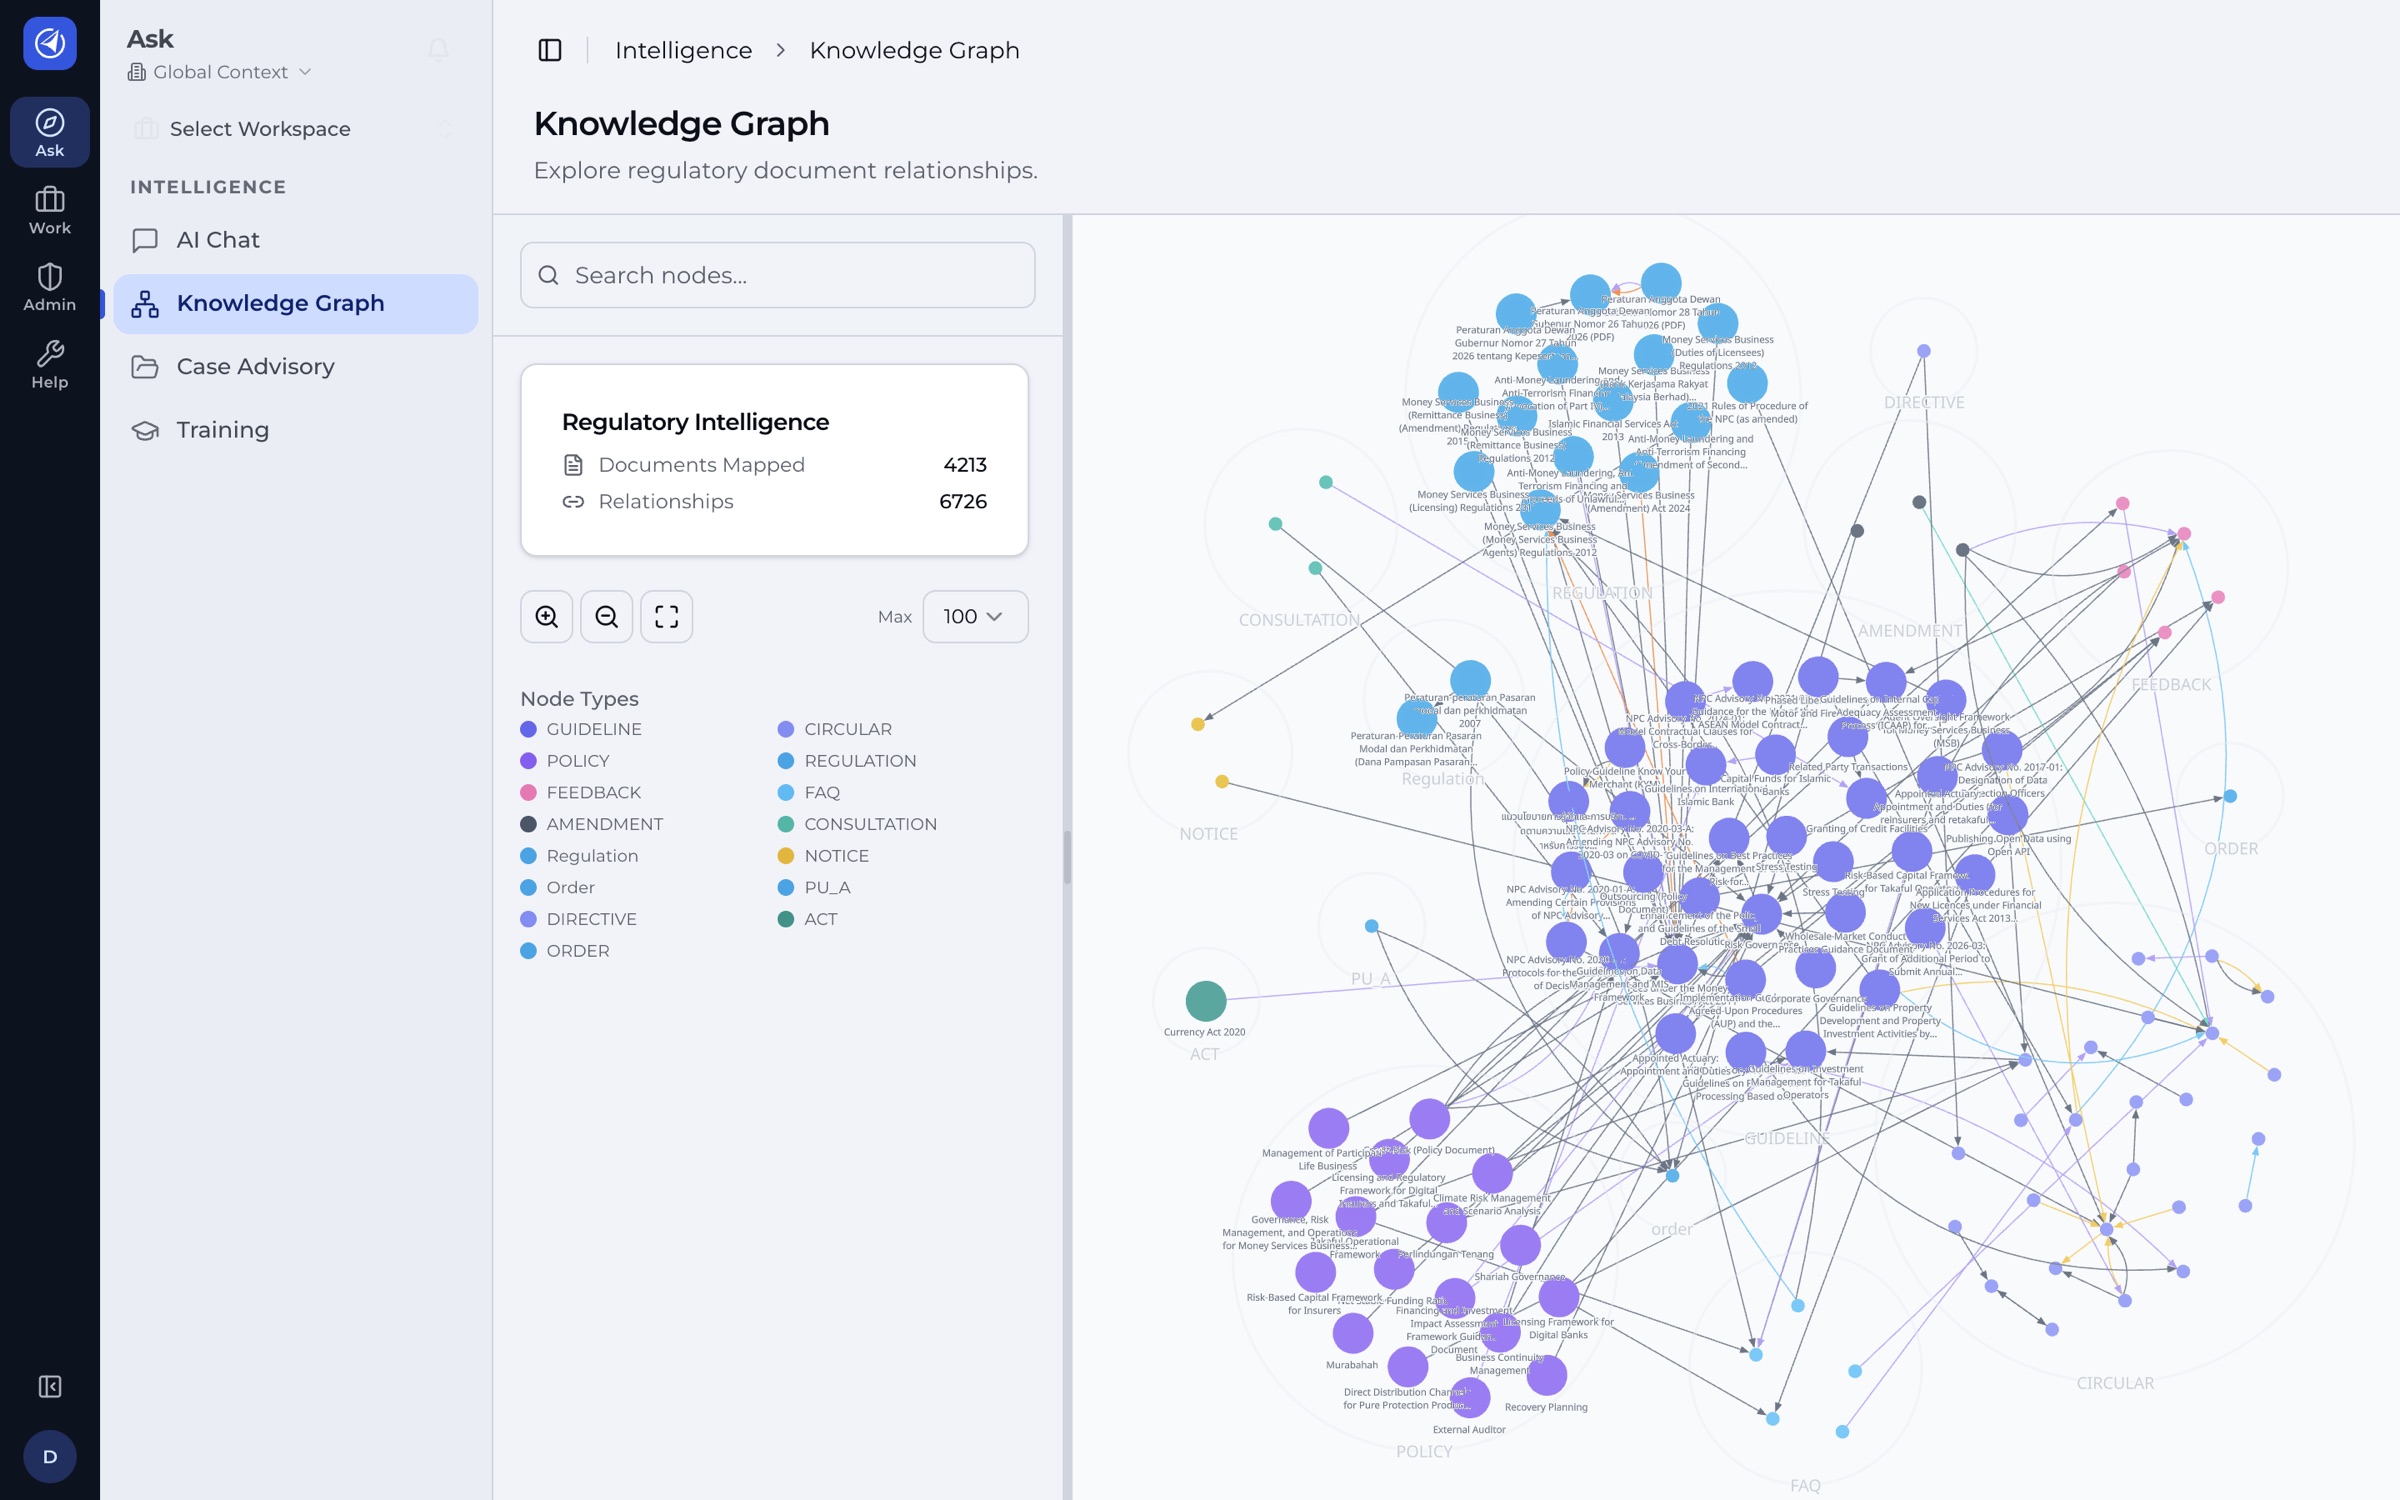
Nakhoda shows you where you stand in two minutes, and exactly how to fix it.
2-minute PDPA risk check
Answer all three to see your result. Nothing you click here is stored.
A quick indicator, not legal advice.
The new rules, in three numbers you can't ignore
people's records, and you must appoint a Data Protection Officer.
Only 10,000 if it includes sensitive data, such as financial details.to report a data breach to the Commissioner.
Then 7 days to tell the people affected. Failing to notify them carries fines of up to RM250,000.maximum fine for breaching the data protection principles.
Up from RM300,000, plus up to 3 years' jail.Source: Personal Data Protection (Amendment) Act 2024 and the Commissioner's 2025 guidelines on DPO appointment and breach notification.
Stop guessing what the law wants from you.
The old way
- Dig through the Act and two new guidelines yourself
- Email a consultant and wait for a quote
- Still not sure which rules apply to you
- Find the gaps when a breach does it for you
With Nakhoda
- Ask in plain English: "Do we need a DPO?"
- Get the answer, with the exact clause, in seconds
- Upload your privacy policy and get a list of gaps
- Fix them before anyone else finds them
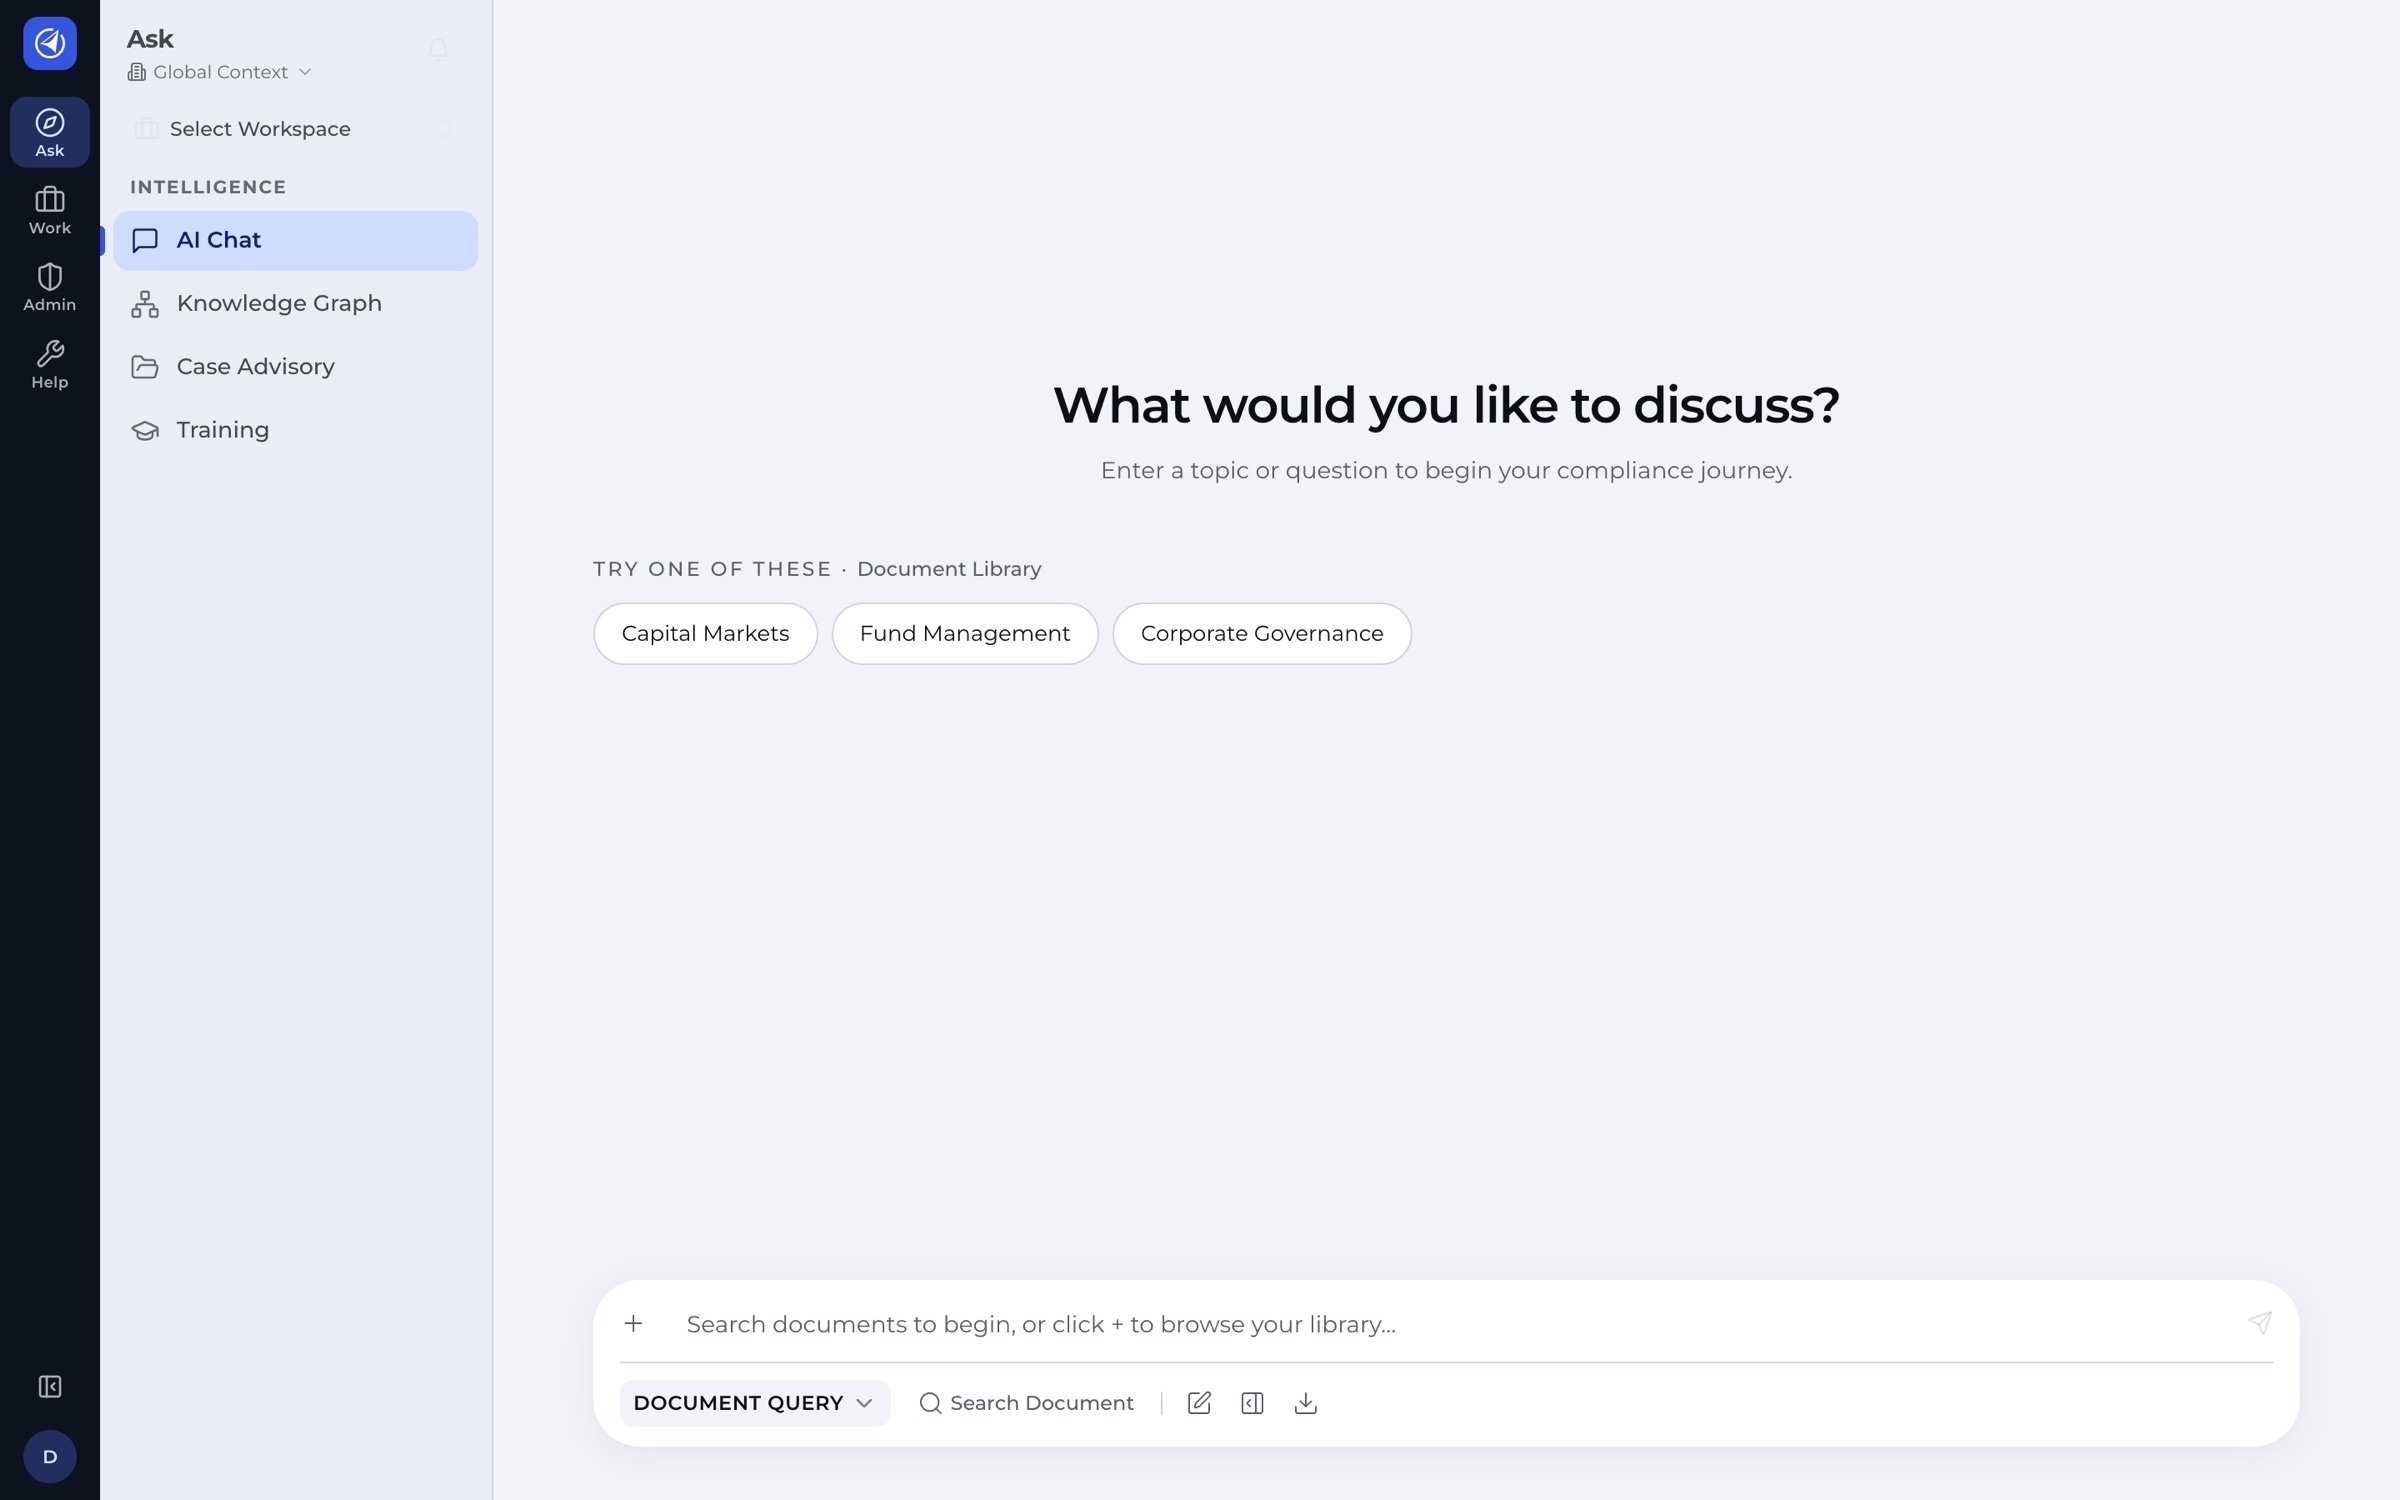
Ask it anything. It shows its working.
Nakhoda Advisory
Example answerYes, most likely. A data controller must appoint a DPO once it processes the personal data of more than 20,000 data subjects. At about 32,000 records, you are above that threshold.
You also need to be able to notify the Commissioner of a qualifying breach within 72 hours, so your DPO should own that procedure.
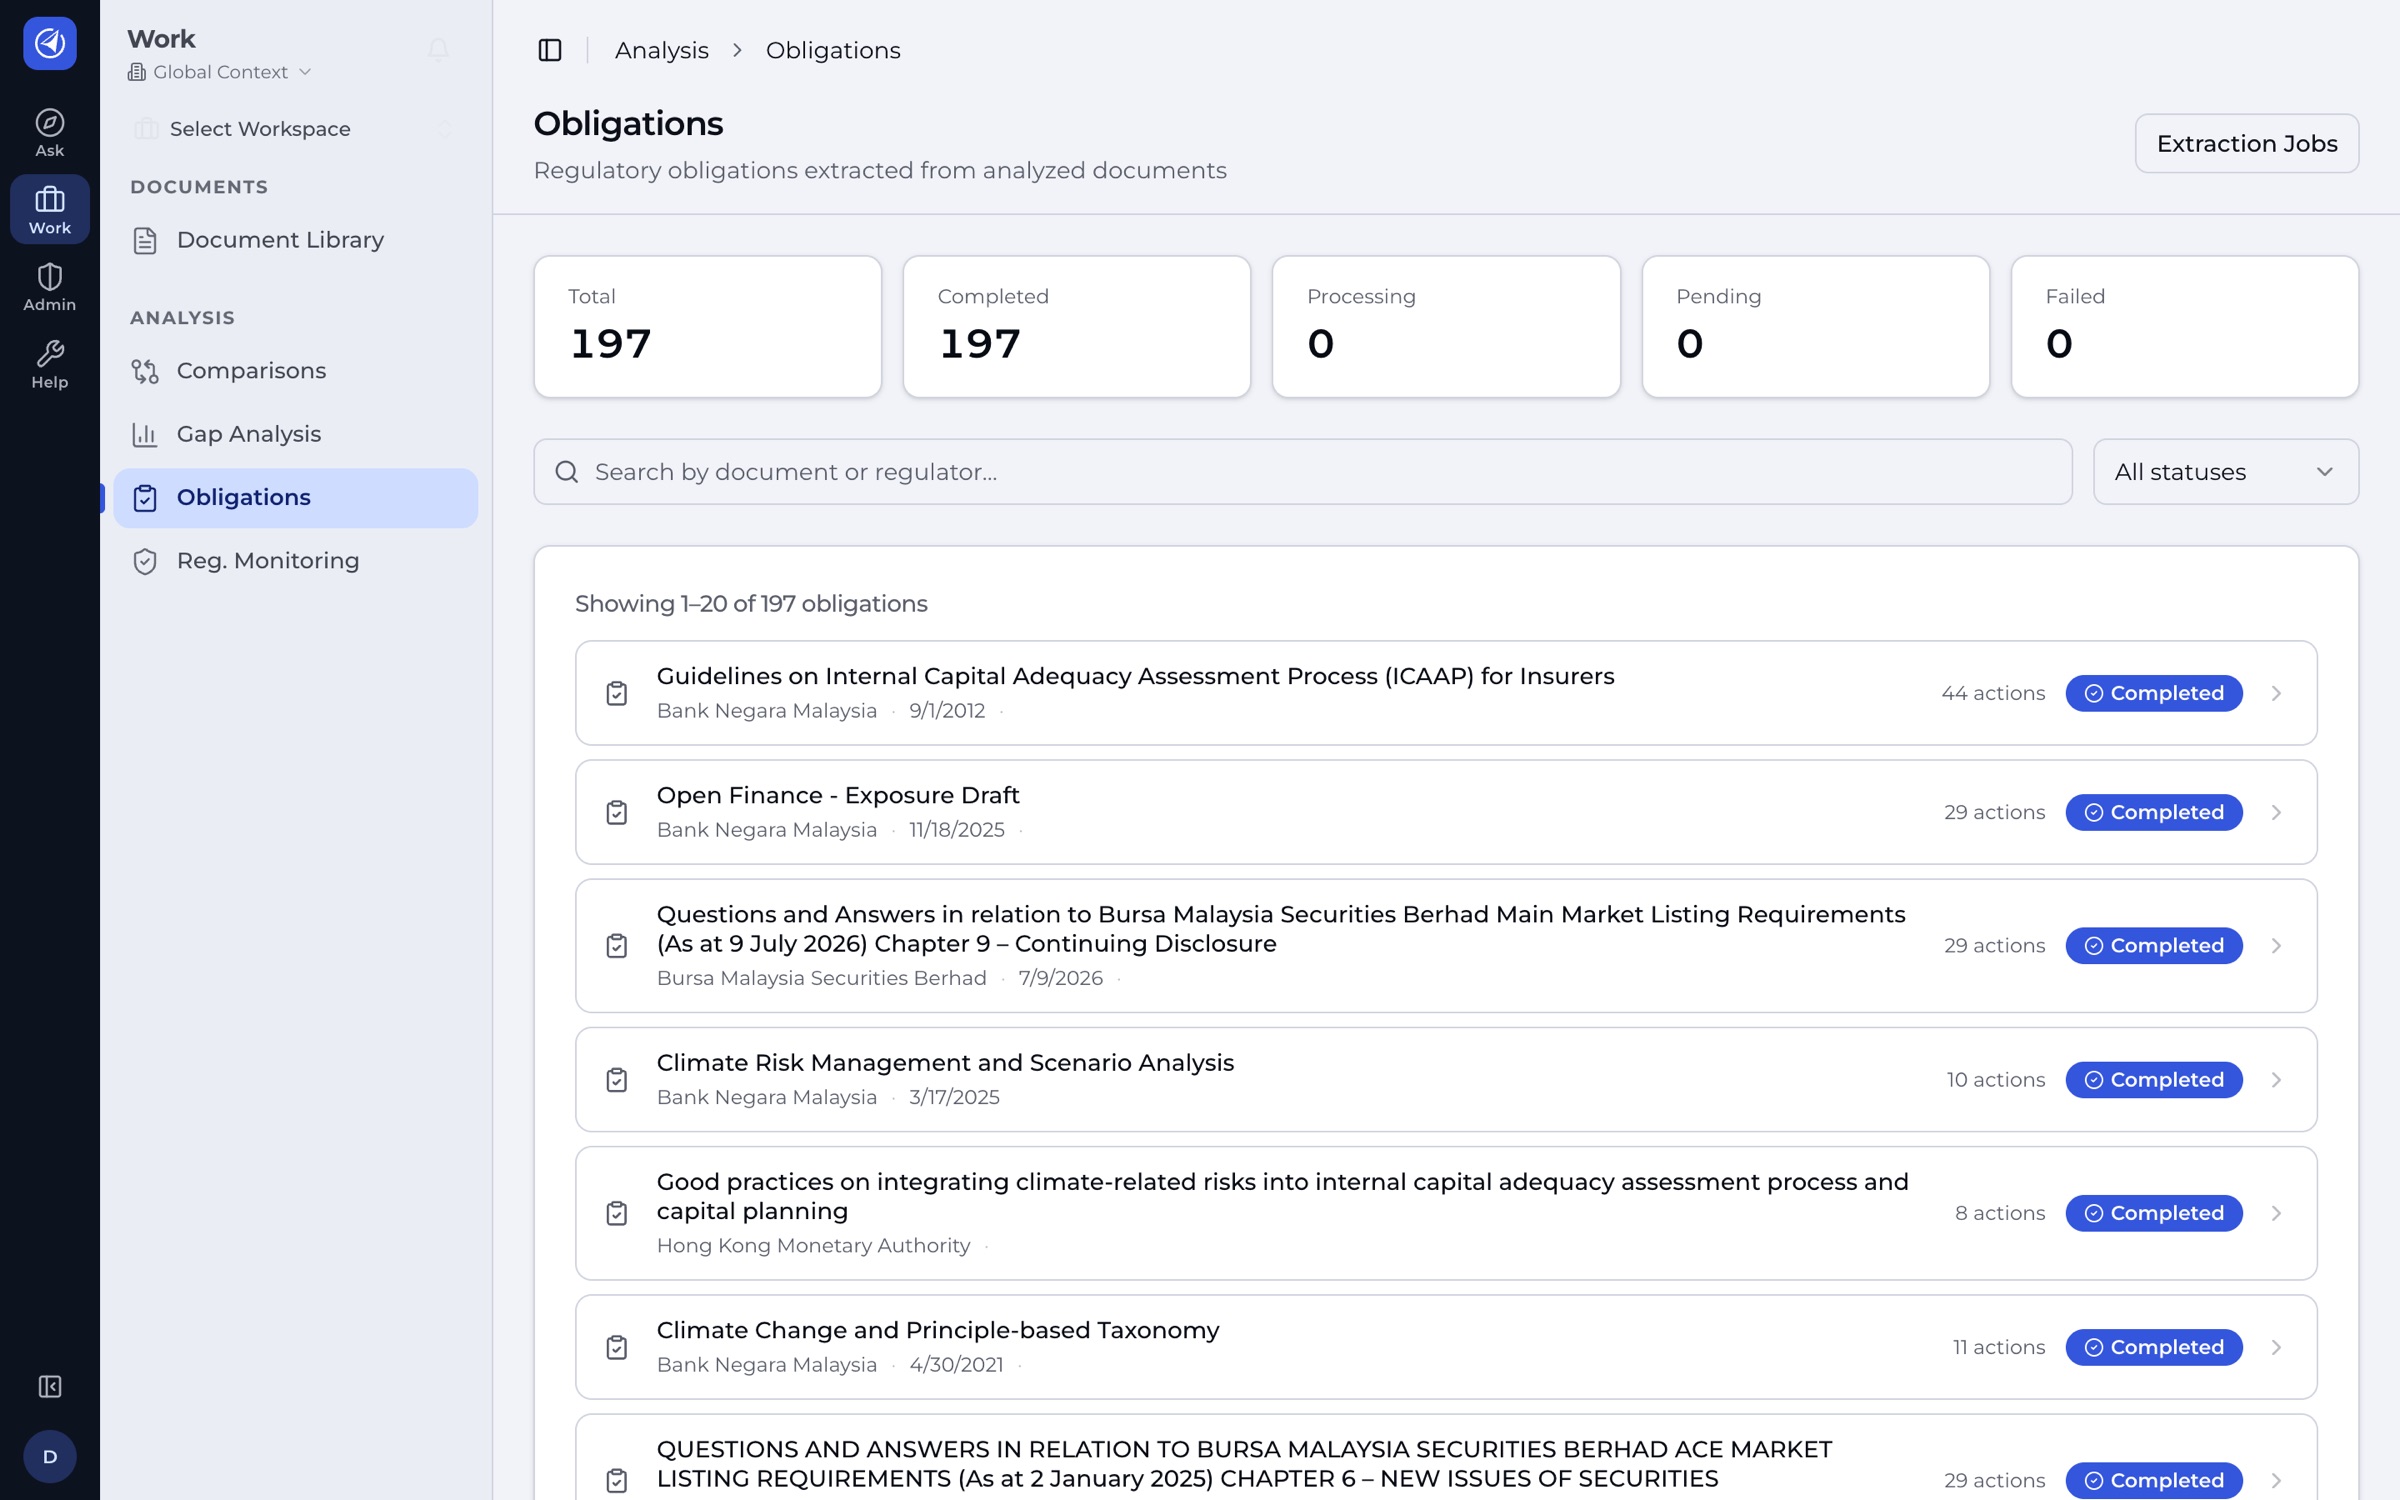
PDPA gap check
privacy-policy-v3.pdf- GapNo Data Protection Officer appointeds.12A
- PartialBreach response has no 72-hour steps.12B
- PartialVendors not bound to security dutiess.9
- MetPrivacy notice in BM and Englishs.7(3)
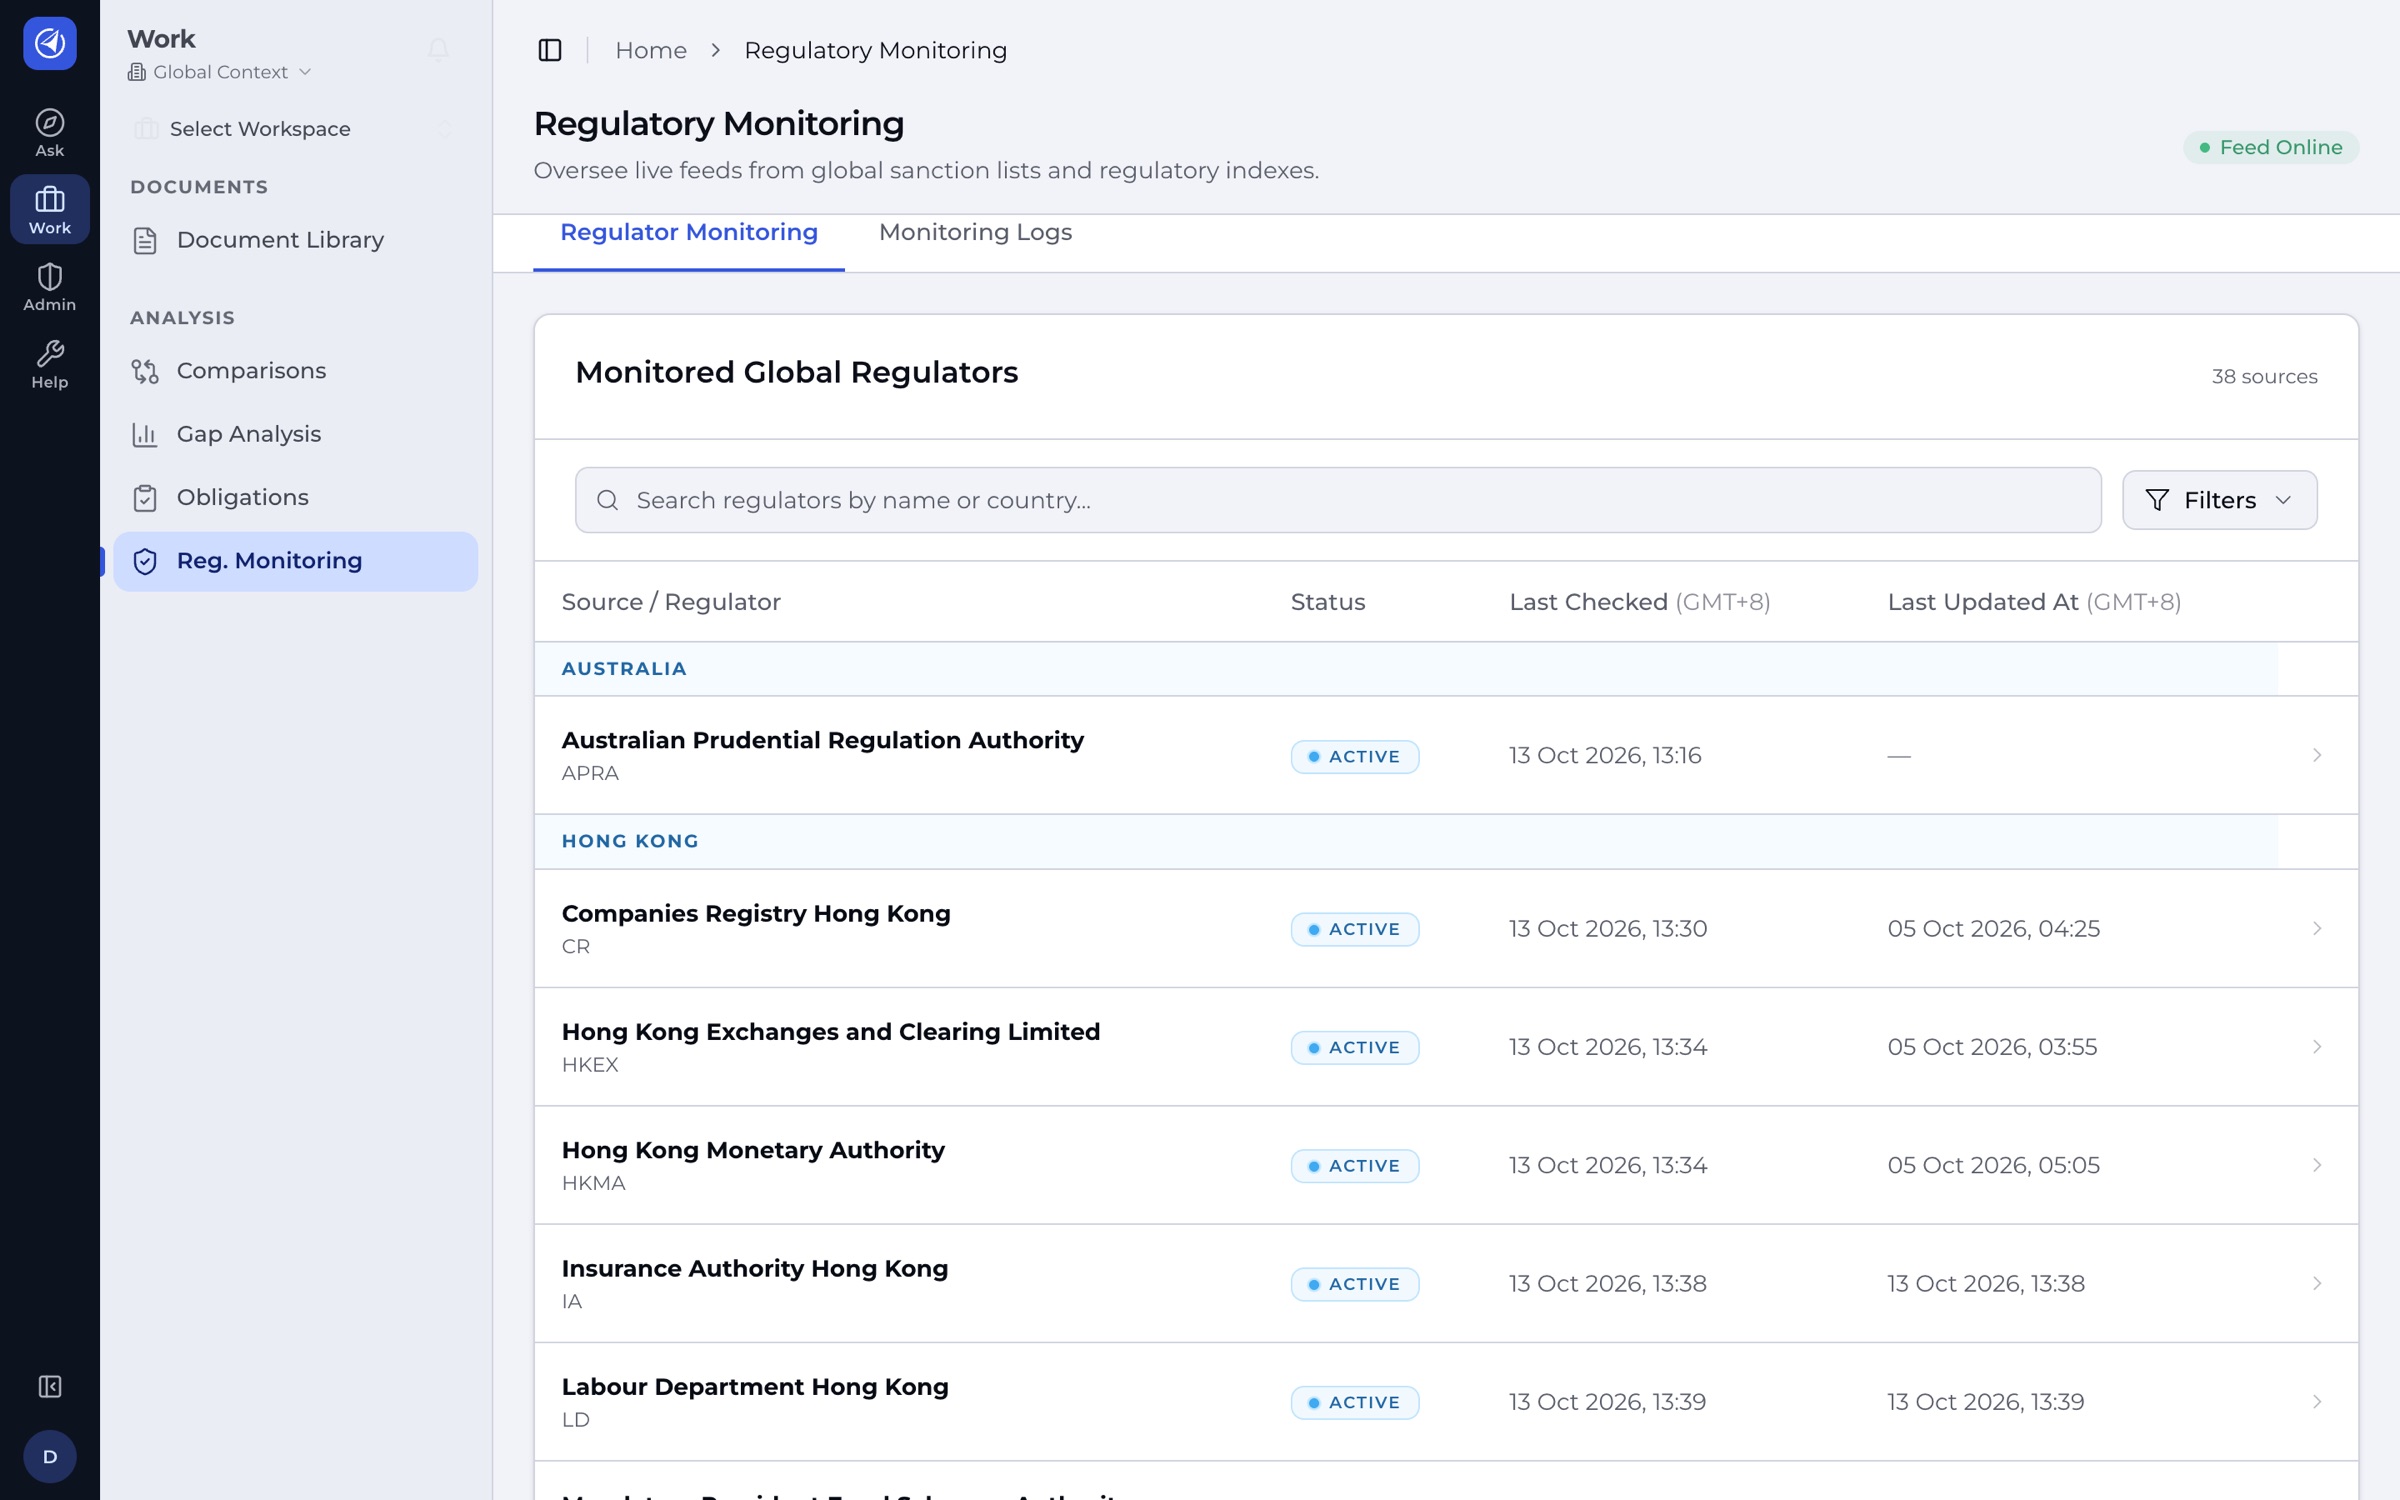
- Also covers:
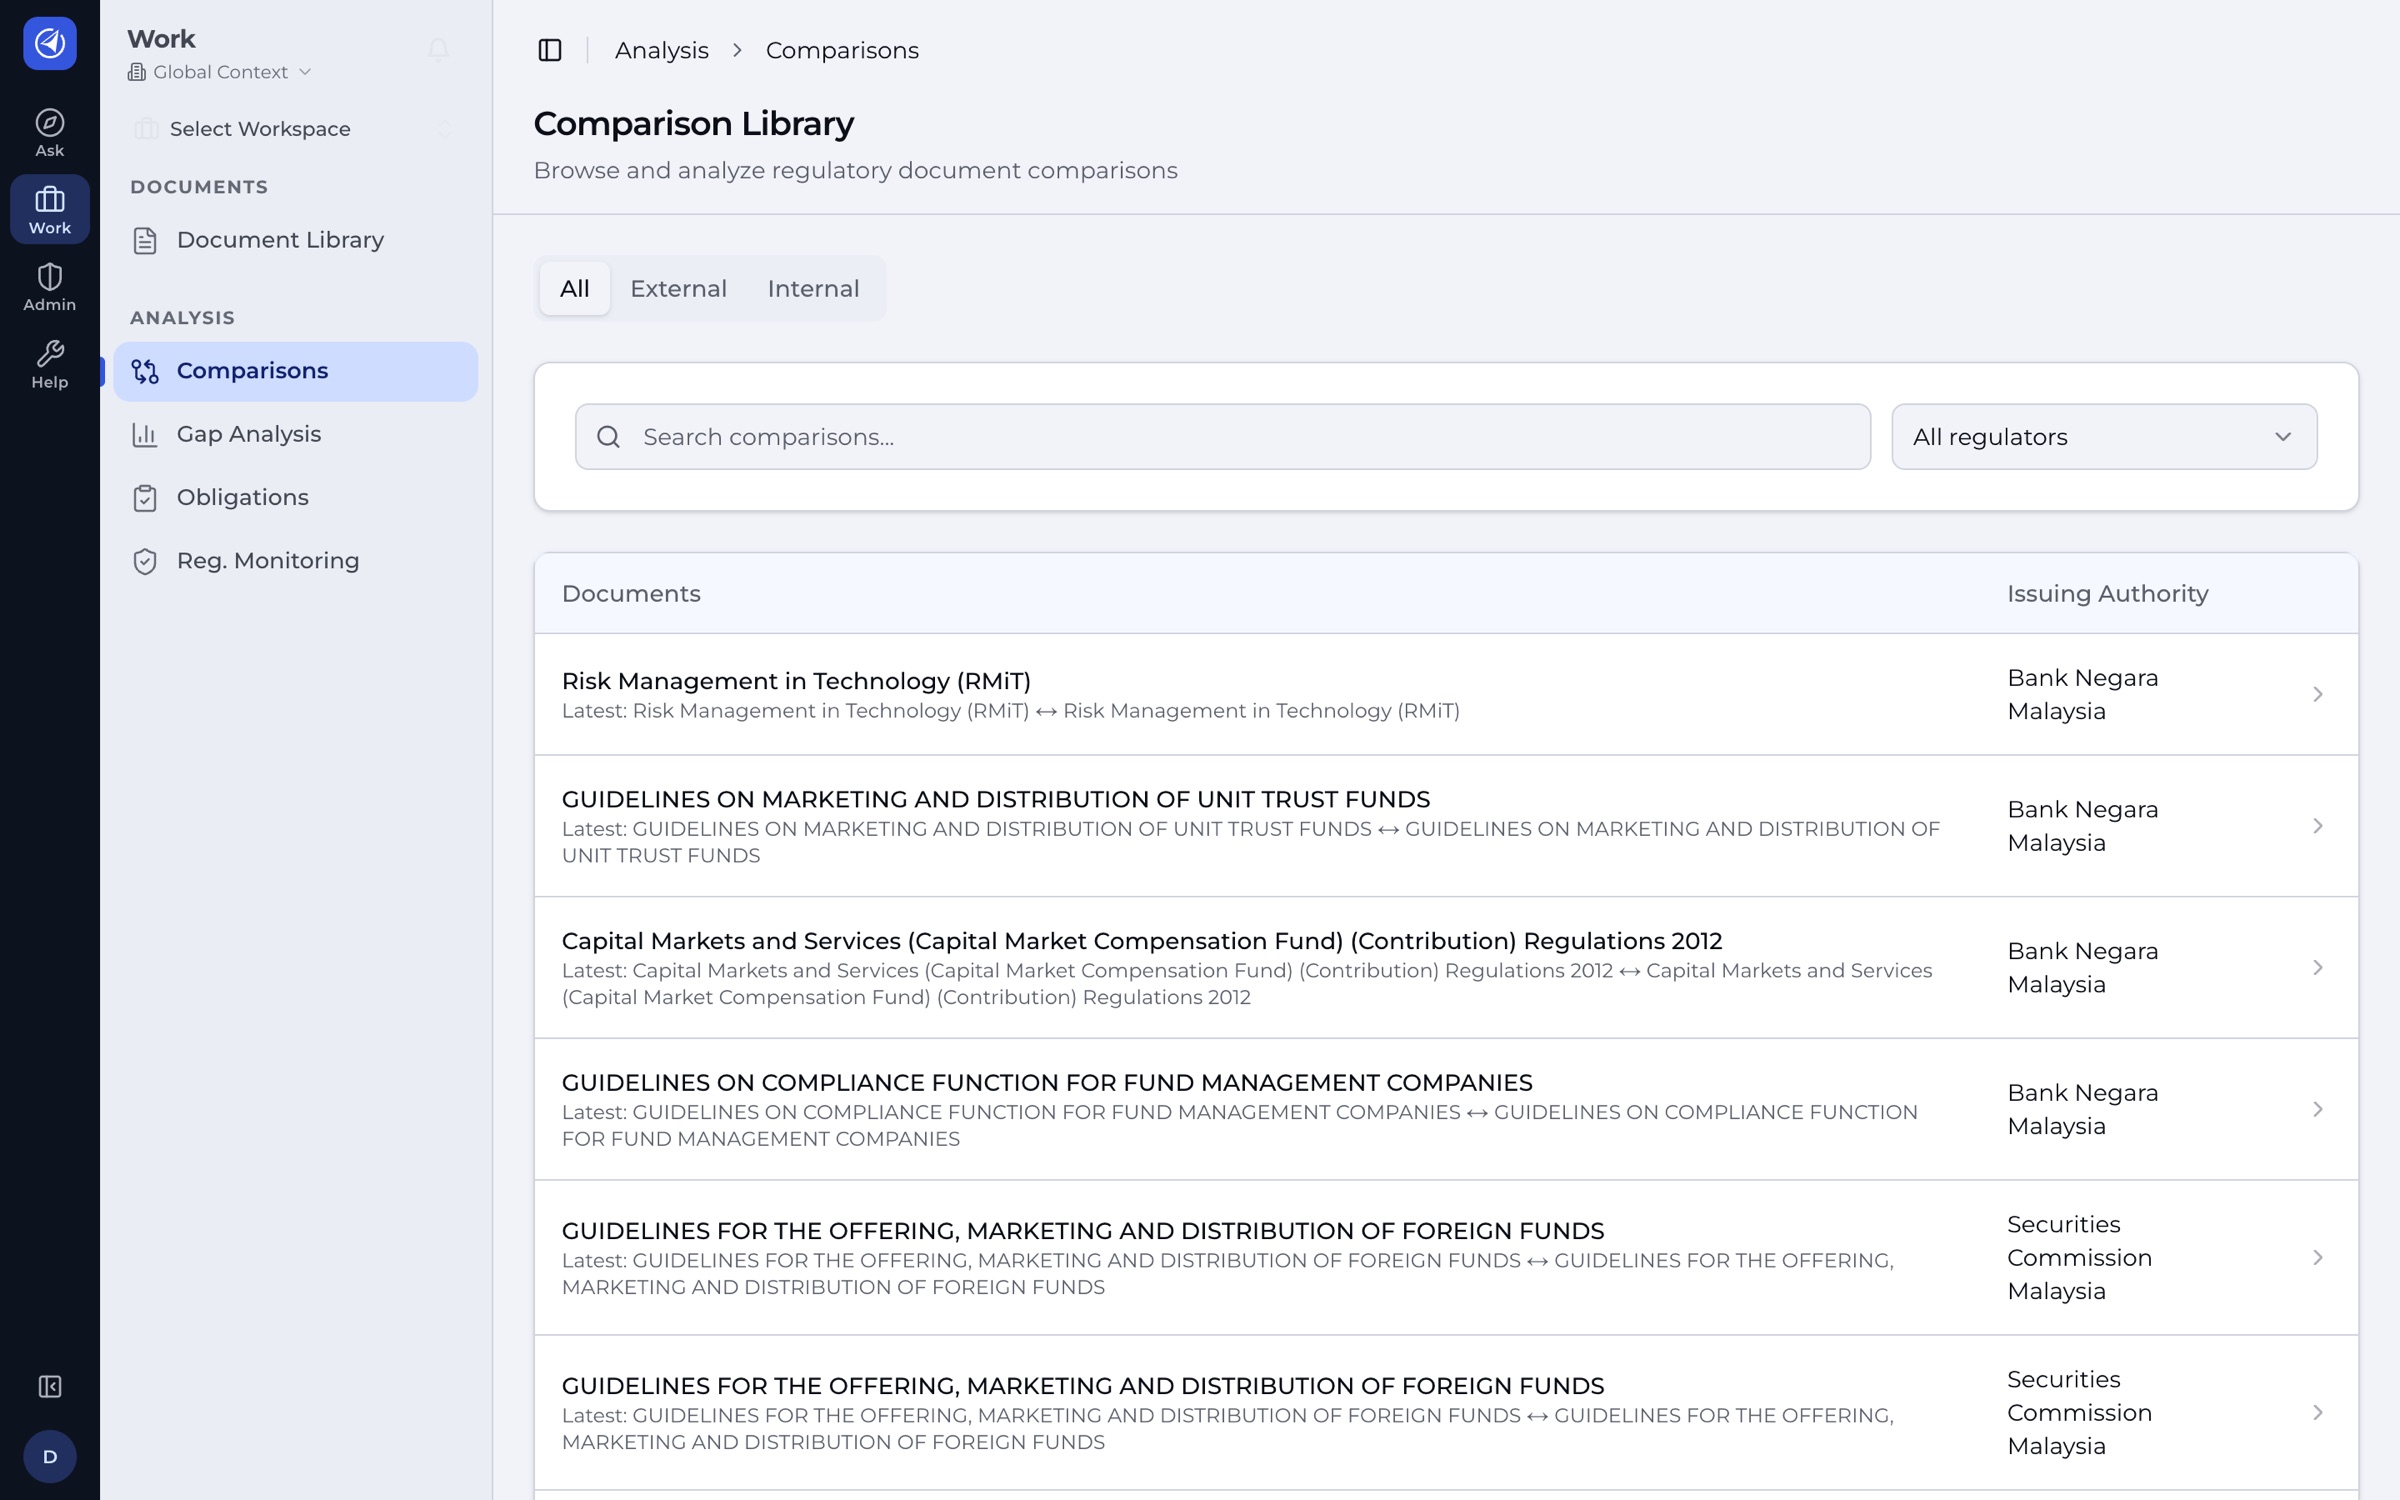
- BNM RMiT
- AML/CFT
- Companies Act 2016
- and publications from BNM, SC, FIMM, LHDN, MACC and MITI
Start free. Fix your gaps today.
Free trial
2,500 creditsAsk questions, run gap checks and export the results. No card needed.
Start free trialStarter
USD 25 / month3,000 credits a month for one user. Or USD 240 a year, which saves 20%.
Try it free firstBanks, insurers and listed companies
Team access and deployment inside your own environment. Start free on your own policy, then email [email protected] when your team is ready.
Start free trialQuestions
Does the PDPA apply to my business?
If you handle personal data in commercial transactions in Malaysia, very likely. Take the risk check above, or ask Nakhoda with your specifics and it will cite the sections that apply to you.
Is this legal advice?
No. Nakhoda shows you what the regulation says and where your documents fall short, with the clause cited so you can check it. For decisions, confirm with your DPO or legal adviser.
What do 2,500 credits get me?
Roughly 100 questions or 15 document gap checks at current pricing.
What happens to the documents I upload?
Uploaded policies are isolated to your workspace, encrypted in transit and at rest in Southeast Asia, and never used to train foundation models. You can delete your documents from your library at any time.